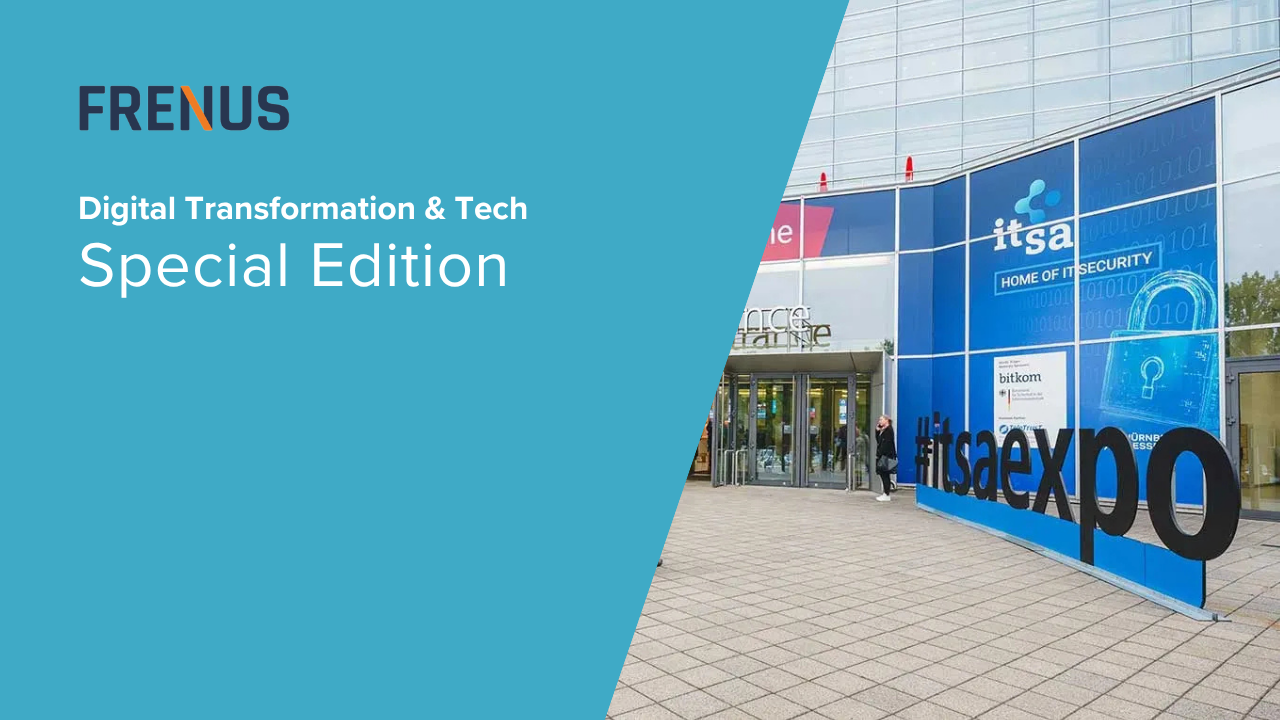
Best of Linkedin: it-sa Expo&Congress 2026
The 2026 edition of it-sa was defined by one question: how do organisations secure AI, prove their resilience and stay sovereign at the same time. AI moved from a topic of interest to an operating risk, with agents, copilots and access rights now treated as security problems in their own right. Regulation set the pace in parallel, as the BSI released Grundschutz++ and NIS2 and the Cyber Resilience Act turned compliance into a demand for evidence rather than assurance.
Date
October 29, 2026
Special - Digital
Thomas Allgeyer

Methodology: Every two weeks we collect most relevant posts on LinkedIn for selected topics and create an overall summary only based on these posts. If you´re interested in the single posts behind, you can find them here: https://linktr.ee/thomasallgeyer. Have a great read!


‍

Listen to our podcast

If you prefer listening, check out our podcast summarizing the most relevant insights from it-sa Expo&Congress 2026

Event Context

  • Exhibitors passed 1,000 for the first time, with more than 400 talks on the programme
  • Dominant themes were AI, cyber resilience, NIS2 and digital sovereignty
  • Buyers want orientation over product pitches, per Rittal and Eplan
  • German buyers ask for independent proof, with FIPS validation and Level 3 requirements raised at Apricorn
  • Short talks at exhibitor stands gave room for detailed questions
  • ITleague found four of seven system houses advising SMEs to take a 24/7 SOC and MDR partner

‍

AI Security and Agent Governance

  • Under 5 percent of granted permissions are used, per CyberDesk
  • AI agents are an identity problem, per BlueFlag Security and Entrust
  • Netskope asks what data agents access and who is accountable
  • Exeon launched AgentGuard to monitor AI agent activity
  • Microsoft Purview sessions covered securing autonomous agents and data
  • KPMG built a deepfake from a visitor's recording in 60 seconds
  • Vanta won the IT Security Award 2026 in GRC and Strategy
  • Plat4mation presented its ServiceNow AI Control Tower approach

‍

Digital Sovereignty

  • German firms choose European cyber vendors as a deliberate buying decision
  • BRANE: server location alone does not guarantee data sovereignty
  • noris network set out when IT services are truly sovereign
  • Secunet, DCSO and Tenzir keep raw data at the edge in one stack
  • Pyramid Computer and Scality showed NIS2-compliant European storage
  • OpenCloud.eu demonstrated live EUDI Wallet login
  • The Cyber Thought Leaders Dialogue stressed shared European responsibility

‍

Regulation and Compliance

  • BSI published Standard 300-1 on Grundschutz++
  • BSI confirmed a five-year transition for the old Grundschutz
  • Open points: no versioned audit reference and scattered requirements
  • Cyber Resilience Act reporting starts with a 24 hour early warning
  • FOSSA showed SBOM and disclosure tooling for CRA compliance
  • A keynote argued resilience must be measured, not claimed
  • HiSolutions finds tools alone cannot solve resilience problems

‍

SOC, MDR and Incident Response

  • Acronis named alert fatigue, OT security and tool sprawl as top concerns
  • Comtrade: clients want fewer, better integrated tools
  • eyeT and ForeNova debated where agentic AI should stop in the SOC
  • Cyngular contained PHP2Shell in 27 minutes, with 9 of 37 servers exposed
  • SecuSeek: 30.4 percent of .de sites with visible PHP stayed vulnerable
  • SVA and Cisco ran the Worst Day game to test readiness
  • Incident response needs predefined roles, not improvisation

‍

OT and Industrial Security

  • SCALTEL calls OT security a prominent theme
  • Siemens premiered a unified, AI-accelerated IT/OT security architecture
  • SINEC Security Guard prioritises OT vulnerabilities by asset inventory
  • Siemens, NVIDIA and Palo Alto Networks anchor trustworthy industrial AI
  • OPSWAT showed secure data exchange across IT, OT and cross-domain
  • FoxIO disclosed three GoAhead TLS flaws, rated CVSS 9.1, 7.4 and 5.9

‍

Product Launches and Partnerships

  • Sophos unveiled four XGS firewalls and a dedicated NDR appliance
  • NCP engineering showed a mobile solution approved for VS-NfD
  • Bundesdruckerei and genua demonstrated cloud collaboration at VS-NfD level
  • Secunet, DCSO and Tenzir turned a letter of intent into one stack
  • Hornetsecurity, N-able and LocateRisk exhibited across three booths
  • SIGNL4 integrated mobile alerting with Acronis
  • OMNINET merged ITSM and GRC around a new MCP server

‍

Cryptography, Identity and Trust

  • Post-quantum deadline equals Q-Day minus your migration time
  • Quantum Key Distribution progress impressed a returning visitor
  • IDEMIA positions its SPHERE HSM as the hardware root of trust
  • Sandgrain presented IC-based authentication for IoT connections
  • A keynote argued negotiation is the one unaudited security discipline
  • ENISA reported 48,000+ new vulnerabilities in 2025, up 22 percent

‍

Subscribe to newsletter

Subscribe to receive the latest blog posts to your inbox every week.

Please confirm your GDPR consent to join our mailing list.
By subscribing you agree to with our Privacy Policy.
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
No items found.

Want to see the posts voices behind this summary?

This roundup brings you the Best of LinkedIn on it-sa Expo&Congress 2026:

‍